Aegis
product deep dive

The AI red teamthat fights like a human.

An attacker who lands in your app does not stay there, and neither does Aegis. Autonomous agents test the application; the operating system, infrastructure and network are tested in their own modes. Every finding graded by its evidence. An attacker's view in hours, not weeks.

Open source·Self-hosted or hosted·Bring your own LLM
02THE GAPthe problem
8%

is how much of your attack surface a quarterly engagement actually covers.

Production code changes hourly. Dependencies update daily. A single pull request rewrites your topology. Your last pentest (four to eight weeks, $15k-50k) describes a system that no longer exists.

Coverage has become a percentage. It should be a date.

“Can I get a credible attacker's view on the release I'm about to ship?”

Q1 · annual/stale/report aged 60 days on delivery$15k-50k per engagement
03ALTERNATIVESwhy current tools fall short

Pentests are periodic. Software is continuous.

Scanner noise

known-bad lookups · low reasoning

Findings lists still require expert triage before a team knows what is actually real. The human triage cost dwarfs the scan cost.

Stale reports

periodic windows · evidence ages fast

An engagement produces a snapshot, then the system changes before remediation completes. The PDF is out of date on delivery.

Human bottleneck

headcount-bound · procurement cycles

Senior testers are scarce; coverage expands only by adding people and calendar time. Doubling coverage means doubling the bench.

The gap isn't detection. It is validated, reproducible adversarial evidence at the speed of delivery.

scanner/noise/triage cost dwarfs the scan costcoverage = headcount-bound
04WHY NOWwhy now

Three curves crossed at once.

reasoning quality

Models now construct full exploitation paths end-to-end, without supervision.

tool-use maturity

Agents chain proxies, shells and analysers reliably; the scaffolding succeeds more than it fails.

token economics

A full assessment moved from experimental to routine. Over 10x cheaper in eighteen months.

None alone made this category. Their arrival together did, and the window is measured in quarters, not years.

2025+/inflection/reasoning x tools x cost convergeearly-mover window: quarters
05WHAT IT ISwhat aegis is

Not a scanner. An autonomous red team that validates what it finds.

PlanProbeExploitValidateReportAudit
A

A swarm, not a scanner

Hundreds of autonomous agents reason, plan and execute tools against your stack. Every call, token and dollar is audited with provenance.

B

Four layers, one engagement

Application, operating system, infrastructure, network. The same run crosses the boundaries an attacker crosses, and one CLI flag puts it on every pull request.

C

Mapped to the rules you live under

Every finding tied to OWASP, MITRE ATT&CK / ATLAS / D3FEND, NIST CSF and AI RMF, plus your sector rules: PCI DSS 4, RBI, UAE Central Bank.

on every PR/gate/working PoC attached, not a suspected bugbounded by compute, not headcount
06ONE RUNproduct in action

From suspicious behavior to validated exploit.

One run, one chain of reasoning, one evidence package your team can defend.

  1. 02:13

    Detect

    Payments API response shape repeats across user contexts.

  2. 02:14

    Investigate

    Sibling endpoints inherit the same authorization pattern.

  3. 02:18

    Prove

    A PoC moves a small balance between test accounts.

  4. 02:18

    Frame

    Impact is translated into transaction and regulatory exposure.

  5. 02:41

    Descend

    The exploit path ran through a credential in app config: the host config audit follows it down.

  6. 08:30

    Report

    Every finding labelled with how it was tested and how strongly it is proven.

The interesting word isn't autonomous. It is reproducible.

single run/audited/6 steps · 0 humans paged · app to host in one chain~$0.02 end to end
07WHAT YOU GETwhat the team receives

Not a bug list. A defensible finding.

finding.log
run.log
target:payments-api
finding:authorization_bypass
endpoint:POST /api/v1/payments/transfer
exploit:test_A to test_B · amount=1.00
severity:CRITICAL
verdict:REPRODUCED
evidence:req/res · PoC replay · owner
Security
Severity, confidence, and the full exploit path.
Engineering
Affected code path and exact reproduction steps.
Compliance
Mapped framework and a complete evidence trail.
Leadership
Business impact in plain English, not CVSS.
1 finding/4 readings/security · engineering · compliance · leadershipno rewriting it three times
08COVERAGEcoverage

Attackers do not respect your layers.

  1. 01

    Application

    The code you ship and the endpoints it exposes.

    Mode
    Agentic engagement
    Evidence
    Validated proof-of-concept, replayable
    • Web apps
    • REST + GraphQL APIs
    • Mobile (Android, iOS)
    • Source code (whitebox)
    • LLM endpoints
    • Agentic AI workflows
    What it finds
    • Broken access control proven across two accounts the agent created
    • Injection chained to data the agent actually retrieved
    • Leaked credentials graded against the vendor blast radius

    A credential in application config is an operating-system door.

  2. 02

    Operating system

    How the host and its containers are configured.

    Mode
    Static configuration audit
    Evidence
    The configuration text itself, 27 checks
    • SSH (sshd_config)
    • TLS termination
    • Dockerfiles
    • Kubernetes and compose
    • Environment files
    What it finds
    • Root login and password auth left enabled on SSH
    • Container running privileged, or mounting the Docker socket
    • A real secret baked into an image layer

    A privileged container is a route to everything the host runs.

  3. 03

    Infrastructure

    The software the host is running, and its version.

    Mode
    Passive CVE correlation
    Evidence
    The version the target disclosed itself
    • nginx and Apache
    • OpenSSL
    • Tomcat
    • Microsoft IIS
    • PHP runtimes
    What it finds
    • A disclosed OpenSSL build inside the Heartbleed range
    • An nginx version matching a published advisory
    • A stack that announces its exact version to anyone who asks

    A known-vulnerable service is a foothold that needs no zero-day.

  4. 04

    Network

    What answers on the wire, and how it negotiates.

    Mode
    Gated active probe
    Evidence
    A completed handshake, consent on record
    • Open TCP ports
    • TLS protocol negotiation
    • Certificate validity
    • Service banners
    What it finds
    • A listener that still completes a TLS 1.0 handshake
    • An expired certificate on a live port
    • A banner handing an attacker an exact version to look up

Every finding at every layer carries a CWE. So all four speak one language: the same OWASP categories, the same ATT&CK techniques, the same clauses. Not four tools that each describe the same host differently.

whitebox + blackbox/replay/each finding validated against the targetreproduced / not / no-poc
More capabilities

The rest of what ships today.

Tech fingerprint

Detect the stack, recommend the specialist.

22technologies, 7 categories
How it works

Response headers, cookie names, body markers, and well-known paths identify what the target actually runs, then the matching specialist agent is recommended for it.

  • Confidence is earned: confirmed needs two independent signal categories
  • Every match carries the signals that produced it, so no recommendation is silent
  • 26 specialist skills reachable, validated against the real skill catalog
LLM red-team

OWASP LLM Top-10 as a runner.

18probes, 9 categories
How it works

A pinned probe corpus driven at any chat endpoint with deterministic detectors by default. The same scope guard and finding lifecycle also drive live cross-tenant RAG isolation and tool/agent authorization probes, and an opt-in model-assisted judge catches compliance no pattern can key on, clearly labelled apart from every deterministic hit.

  • String-match, regex, and refusal-absent detectors
  • SSRF guard refuses metadata/link-local targets and redirects
  • Findings carry a lifecycle: candidate, validated, remediated, reopened
Mobile VAPT

Android plus iOS, library-only.

2platforms (iOS + Android)
How it works

Static audit of manifests, ATS exceptions, exported components, URL schemes, and hardcoded secrets.

  • Stdlib only, no APK or IPA decoding
  • Vendor-prefixed credential regex registry
  • Dashboard analytics segment plus CLI verb
Infrastructure & OS

Three modes, one honest boundary.

3modes: static, passive, active
How it works

Static configuration audit, passive CVE correlation from versions a target already disclosed, and live TCP/TLS probing that stays off until you arm it.

  • 27 config checks across SSH, TLS, Docker, Kubernetes and env files
  • Active probing gated four ways, off by default, consent on record
  • Findings carry a CWE, so they map to OWASP, ATT&CK and clauses
Specialist roster

Sixty skills, loaded on demand.

60skills in the catalog
How it works

Agents do not carry one generic prompt. They load the skill the target calls for, from OAuth flaws and request smuggling to cloud misconfiguration and prompt injection.

  • Loaded at run time, so a scan carries only what it needs
  • The fingerprinter recommends them by the signals it observed
  • A new specialist is a skill file, not a change to the agent loop
Operator toolkit

The tools a human tester would reach for.

6tool families in the belt
How it works

An HTTP proxy, a headless browser, a terminal, a Python runtime, web search, and file analysis, wired into the agent loop inside an isolated sandbox.

  • Every invocation is a typed telemetry event, not a side effect
  • Runs in the sandbox container, never on the dashboard host
  • The same belt the specialist skills are written against
Posture over time

Answer whether you actually got better.

per targettrend, not a snapshot
How it works

Scans of the same target line up against each other: what is fixed, what is new, what came back. Posture is classified per run and charted as a trend, not asserted.

  • Fixed, new, and regressed findings separated by canonical hash
  • Cost and coverage plotted next to severity, per scan
  • Every roll-up reconstructible from the per-event record beneath it
Workspace and governance

Org, project, product, scan.

4levels of attribution
How it works

Findings inherit the business context that decides how much they matter. Criticality on a product escalates its findings; every UI-driven change lands in an activity trail.

  • Company profile turns a medium into a board-level risk where it belongs
  • Per-tenant isolation, with cross-tenant access a time-bounded grant
  • Self-hosted by default: your database, your keys, your network
09VS THE FIELDwhy it is different

Reasoning, validation and audit, in one system.

dimension
scanner
traditional pentest
aegis
Cadence
Continuous
Periodic
Continuous, every deploy
Depth
One layer per tool
Scoped and priced per layer
App to network, one platform
Reasoning
Low
Human expert
Autonomous agents
Validation
Often noisy
Manual
Working PoC attached
Output
Findings list
PDF report
Live reproducible evidence
Scaling
Tool-limited
Headcount-limited
Compute-limited
Auditability
Logs
Consultant notes
Token / tool / cost trail
3 modalities/compare/scanner · traditional pentest · aegisthe part each one is missing
10CONTROLgovernance and enterprise controls

Autonomy you can put in front of a regulator.

Aegis is an offensive system, so governance is a product requirement, not an appendix. Every prompt, tool call, reasoning step and dollar is a typed telemetry record, and each finding carries the chain of inference that produced it.

A senior consultant remembers a fraction of what they did. Aegis records all of it.

enforced on every scan
Deployment
Hosted · self-hosted · air-gapped
Models
Bring your own LLM · policy-controlled usage
Secrets
Vault · 1Password · AWS · no plaintext credentials
Budgets
Per-scan caps · real-time spend visibility
Kill switch
Live, every run
Audit trail
Tokens · tools · findings · dedupe · cost
every action/receipt/operators · regulators · boards see the workaudit = the control plane
11COMPLIANCEcompliance and reporting

The same finding, read as engineering, risk and compliance work at once.

app security
OWASP Top 10
full reasoning
llm
OWASP LLM Top-10
18 probes · 9 categories
agentic
OWASP Agentic T1-T15
anchored to MITRE ATLAS
adversary
MITRE ATT&CK
technique mapping
ai threats
MITRE ATLAS / D3FEND
offense + defense
national
NIST CSF + AI RMF
control alignment
payments
PCI DSS 4
sector mandate
banking · in
RBI Cyber-Security
sector mandate
banking · uae
UAE Central Bank
sector mandate
per finding/map/auto-mapped on write, no manual triageaudit-ready output
12PRICINGpricing

Free self-hosted, forever. Hosted when you need the team around it.

Community
Free
  • 5 scans per month
  • 1 target
  • Basic report
  • Community support
  • Self-hosted only
most popular
Pro
$249/mo
  • Unlimited scans
  • 10 targets
  • CI/CD integration
  • PDF + dashboard
  • Slack alerts
  • Email support
Team
$999/mo
  • Everything in Pro
  • 50 targets
  • RBAC & SSO
  • Compliance reports
  • Priority support
  • Custom rules
Enterprise
Custom
  • Unlimited targets
  • Self-hosted / air-gapped
  • BYO LLM
  • Kill switch & audit
  • Founder-led onboarding
  • Custom SLA

Every tier enforces the same per-scan budget cap, real-time spend visibility, and dollar-per-finding telemetry. The tier governs how often you run, not how the platform behaves on each run.

~$200/per run/full-coverage run, repeatable at marginal costvs $15k-50k per pentest
13CORE TEAMwho is building it

One platform builder. Two security leaders.

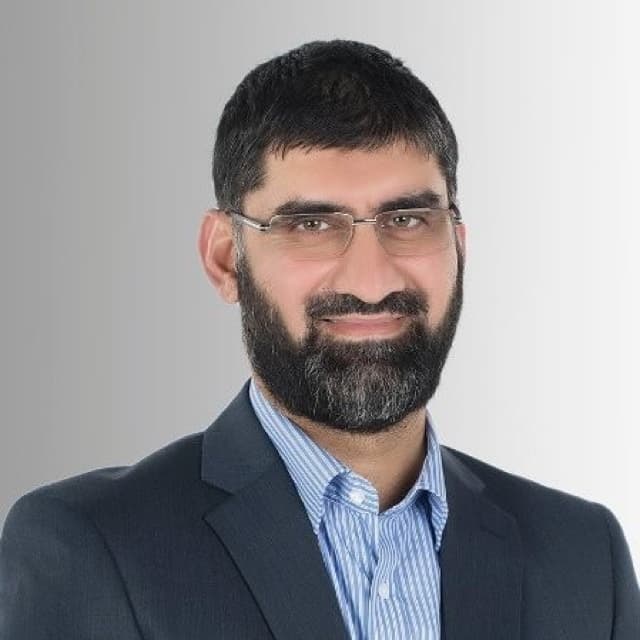
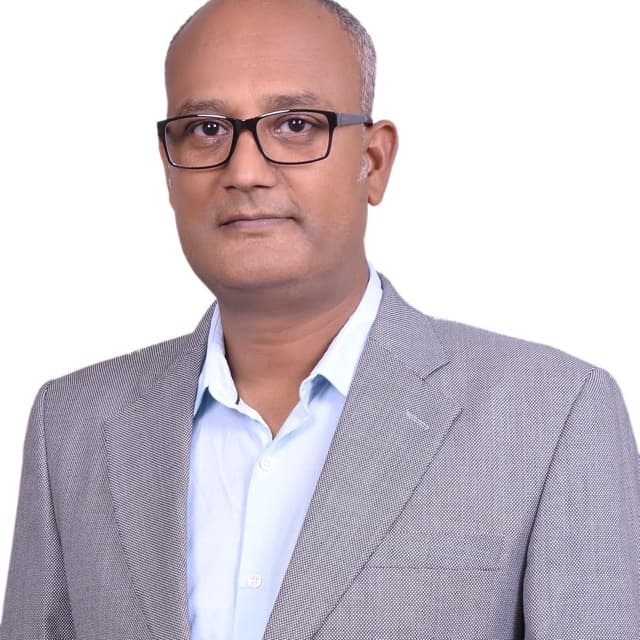
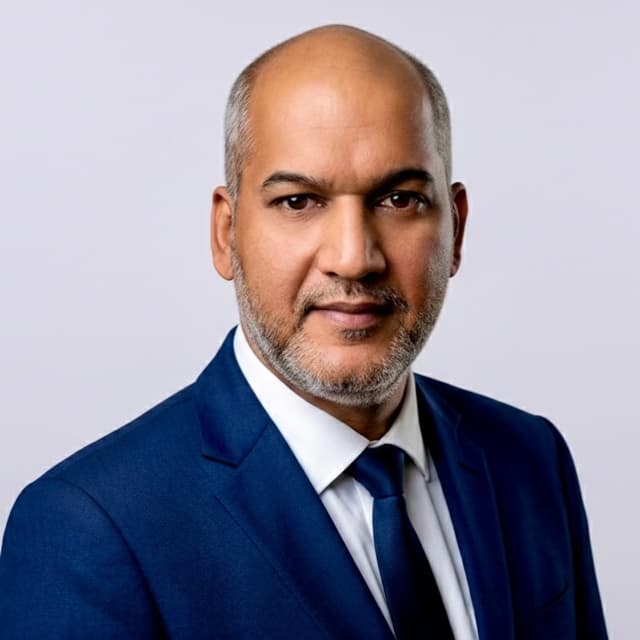
One founder builds the agent platform. Two have spent their careers running the security programmes, and clearing the certification regimes, that it reports into.

Vishal Mishra
Co-founder

Vishal Mishra

Chief AI Officer. Non-Executive Director. Author.

Builds the agent platform: the autonomous testing loop, the evidence pipeline that replays every proof of concept, and the per-call cost ledger underneath it.

Assad Irfan
Co-founder, CISO

Assad Irfan

Cybersecurity transformation leader.

Leads global AI-powered cybersecurity programmes, advising brands and decision makers on strategic, cost-efficient defence. Brings the 360 degree operator view.

in/assad-irfanGlobal programmes
Pankaj Kumar
Co-founder

Pankaj Kumar

Cybersecurity transformation and strategy leader.

Eighteen years of enterprise security transformation, from on-prem through cloud, SASE and ZTNA. Carries the certification side: FIPS, Common Criteria, NIST, USGv6 and VPAT.

in/pankaj-kumarRegulatory and compliance

The people building it are the people who have had to answer for it: to a board, to an auditor, and to a certification lab.

3 founders/build/platform engineering · security programmes · certificationoperator view, not vendor view
14AEGISwhat to do next

Test run against your own surface in under 15 minutes.

Bring one app or API. We run a bounded, instrumented engagement against your real surface, and you leave with validated evidence to compare against your last assessment.

Prove value from a pilot immediately.

The cleanest buying motion is to run Aegis against a real surface and compare the output to your last assessment.

1

Select target

One app, API, or agentic workflow with test credentials.

2

Run Aegis

Bounded budget, bounded scope, fully auditable activity.

3

Review evidence

Validated findings, PoC replay, impact framing, remediation path.

4

Compare

Time, cost, coverage, false positives and usefulness vs. your last pentest.

Pilot success criteria: reproduced findings, lower triage burden, faster evidence, and a credible path to deployment gating.

The category is arriving. The only variable is who runs it first.

bounded/engage/time-boxed · dollar-capped · fully instrumentedcompare the receipts side by side